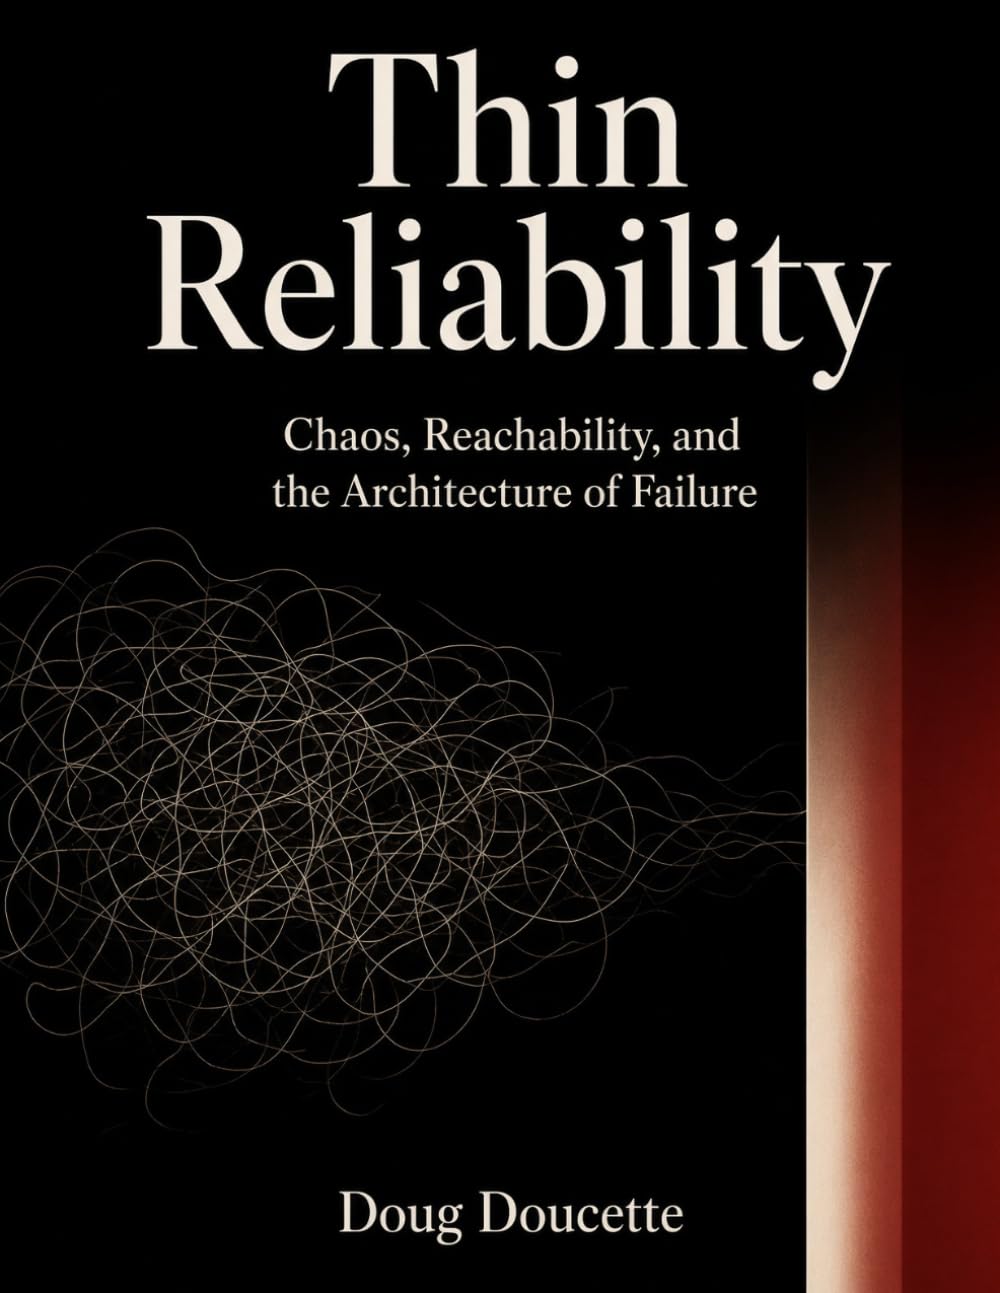
Thin Reliability: Chaos, Reachability, and the Architecture of Failure kindle baixar
de Doug M Doucette
Escolha um formato:
| zip | Baixar grátis |
|---|---|
| rar | Baixar grátis |
| Baixar grátis | |
| mp3 | Baixar grátis |
| audiobook | Baixar grátis |
| kindle | Baixar grátis |
Descrição do livro
Thin Reliability: Chaos, Reachability, and the Architecture of Failure (Doug Doucette, SAIT, 2026) is a short theoretical monograph that sits between classical reliability engineering and chaos theory. It does not replace failure rates, Markov models, fault trees, or demonstration tests. It argues that those tools already compute the right numbers in many cases, but informal practice often misnames what the numbers are about. The governing sentence is: a system is reliable when its chaos remains thin relative to the operational failure set. “Chaos” here is not Lyapunov exponents or strange attractors. It means ordinary reliability instability—component failure, wear, latent defects, imperfect switching, common-cause shocks, incomplete coverage, unrestored age after repair. Thin means that instability can occur without reaching the named loss of function on the stated horizon. Thick means a route into that loss set is already open. Transitional means remaining margin is still positive and shrinking. The book’s target is reliability’s hidden assumption: that a local event is already system failure. That identification is exact for a single nonrepairable item whose required function is its own survival. It fails for redundant, repairable, software-bearing, phased, or safety-critical systems. Two channels can lose one unit while the system stays up. A defect can exist without being activated. Wear can proceed below threshold. Production can continue after protection is lost. Occurrence is not loss. Doucette therefore insists on a well-formed claim: state space, evolution, admissible initial law or repair kernel, projection (the required function), failure set, horizon, model class, and predicate. Two projections of the same hardware can disagree. First-hit reliability and occupancy (availability) are different predicates and can disagree on the same pair. Combinatorial thinness (system-down is not a one-step neighbor) is independent of probabilistic thinness (hitting probability below a tolerance). Graph reach in a constant-rate Markov chain already makes the down set possible on every positive horizon; a numerical requirement is a different statement. Structure is read as architecture. Series systems give every local failure immediate reach. Parallel and k-out-of-n structures defer reach until a remaining cut is completed. The rate of reach, when the failure set absorbs, is an occupancy-weighted sum of jumps that actually enter that set. Adding item hazards is the series formula used off-label on a redundant diagram. Common-cause shocks, failed switches, and some coverage holes are extra entering jumps the block diagram does not draw: they make both-up combinatorially thick without making the shock a series element in probability on a short mission. Repair inside the up set only moves occupancy off dangerous states. Return from the down set is a kernel. As-good-as-new is a statement about which coordinates that kernel resets. High availability is compatible with a poor first passage: fast repair shortens visits; it does not delay the first visit. A test estimates only the rates, lives, and initial mass whose source states it occupies. Item-hours do not bound a system shock the bench never assembled. A declining growth plot does not identify whether a shock, a single-bit rate, or a bad atom of the initial law moved. The running object is a 1-out-of-2 repairable pair with optional common cause and a latent bit. Four claims and three tests on that pair are enough to show that hardware is not the claim. The elementary nonrepairable item remains included and clean. The contribution is a single place to keep required function, routes, and evidence from collapsing back into one word.
Autores populares
Icon Group International (289) Publishing lmgdaw (229) Nikolay Krechet (123) Kennie B Journals (118) Charles Nehme (107) webmarbook design (97) Riddler Books (94) Ondrej Sarek (87) Jillo Trukudo (77) dkdesigns Publishing (76) Mint and Cherry Notebooks (74) Maria Emmrich (73) Just Visualize It (72) Various (69) Moonpeak Library (67) Reynhard Boegl (67) Bettina Schipp (66) DARE AGRO (66) matlasor Sticker's (66) Talor Press (66)